As part of the VMware Cloud Foundation (VCF) 9.1.1 release, consuming NSX Virtual Private Cloud (VPC) has gotten simpler, especially for environments using traditional VLAN-backed networks. In VCF 9.1.0, users already had the ability to configure a VPC using a Distributed Transit Gateway (DTGW) and Distributed VLAN through the NSX Virtual Network Appliance (VNA), but this still required configuring NSX Tunnel Endpoints (TEPs) on each ESX host.
With VCF 9.1.1, the networking workflow has been further simplified with a new VLAN-backed VPC option. While it still uses DTGW and VNA, TEPs are no longer required, removing additional network requirements such as a larger MTU. As a result, environments that previously could not meet the networking requirements to configure a VPC can now deploy and consume services such as vSphere Kubernetes Service (VKS) and VCF Automation (VCFA).
It is also important to understand the different VPC consumption options and their constraints. The following table summarizes the capabilities and limitations of each option.
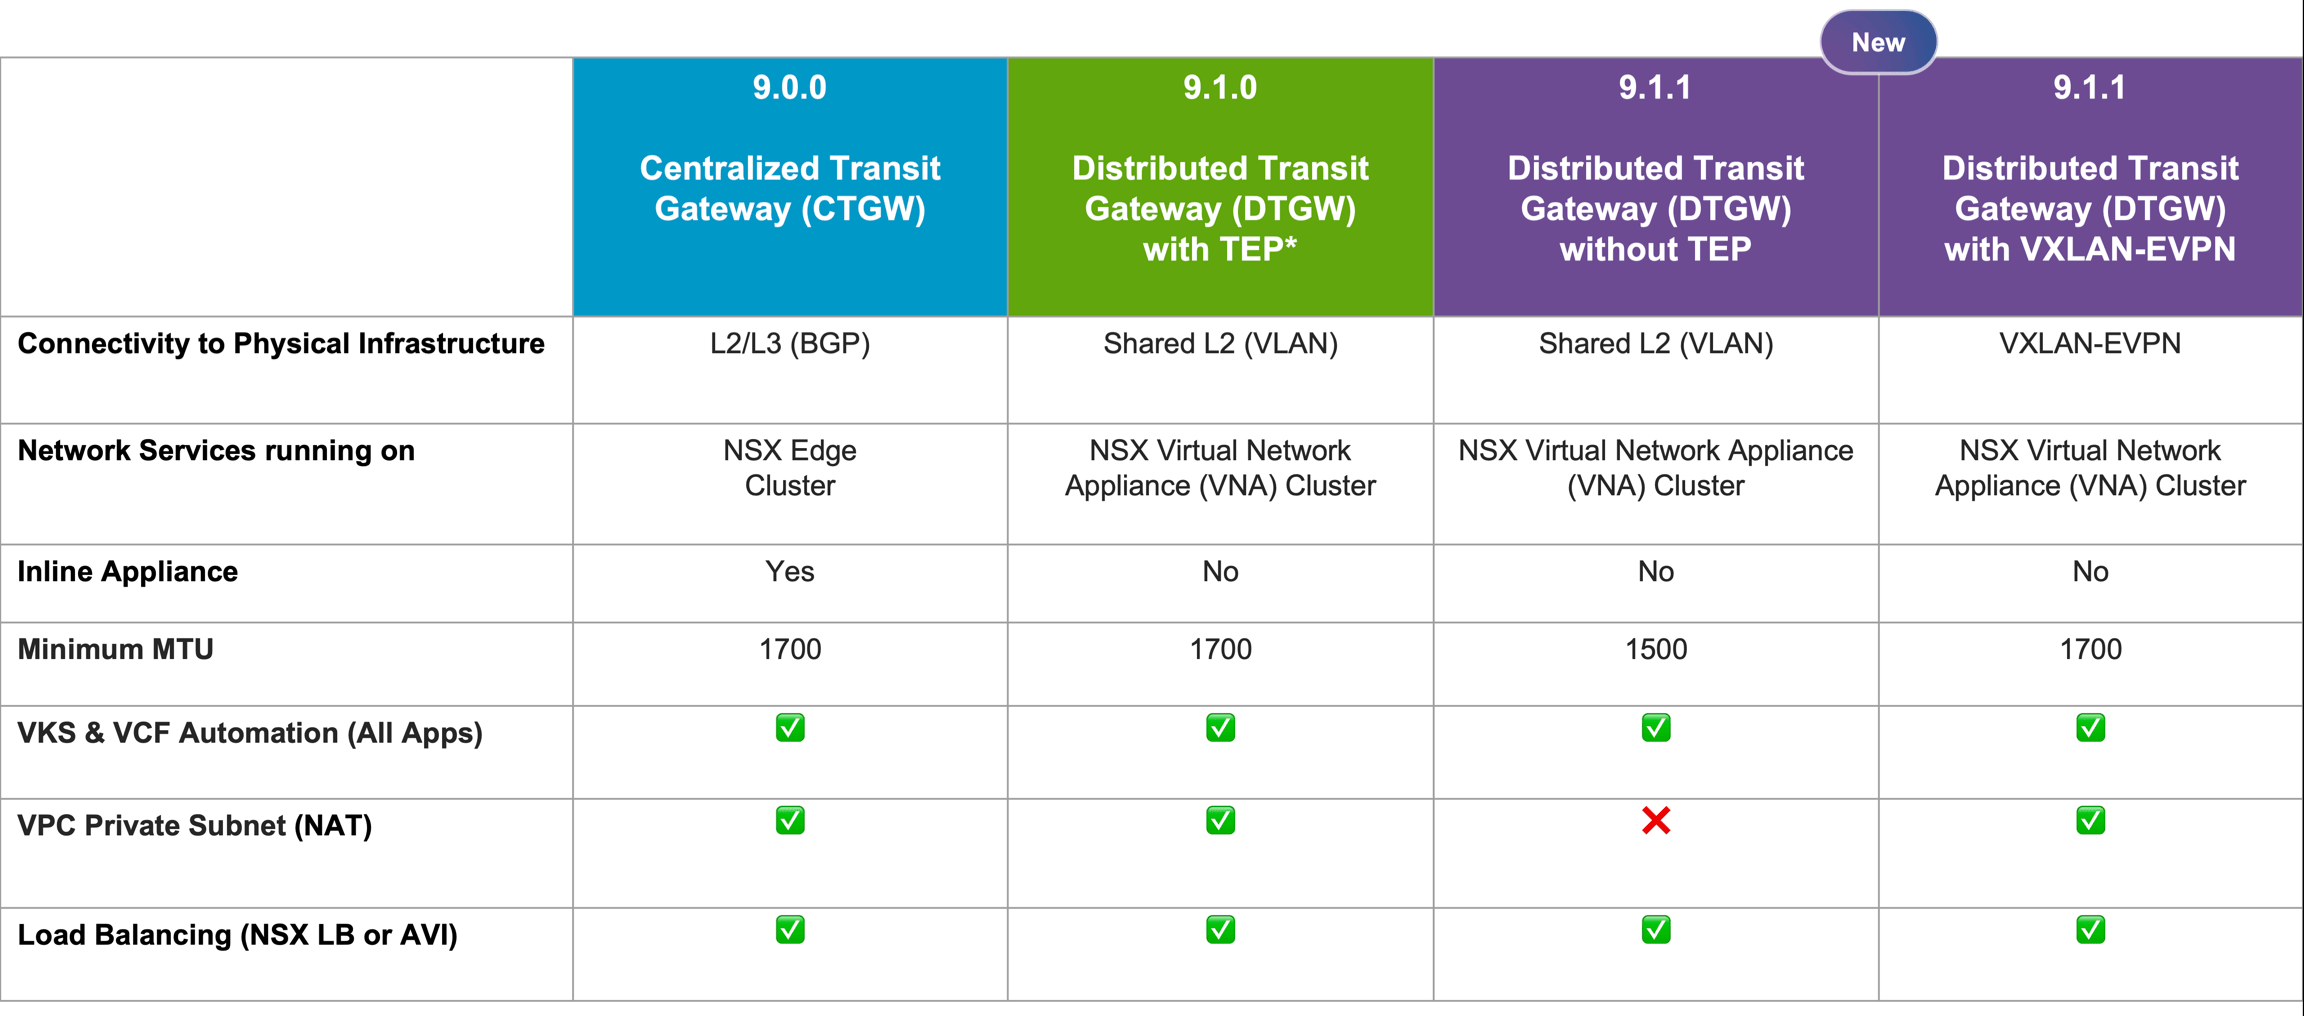
Note: DTGW with TEP was possible with VCF 9.0.0 but there was no support for VCFA until VCF 9.1.0.